Features
Varsto is built around one idea: your files live on devices and storage you choose, every copy is ciphertext, and the app keeps honest, signed bookkeeping of where every block is. The features below follow from that. Everything described below exists today; the list at the end is what is designed and documented but not built. The Use cases page tells the same story from the user's side, one situation at a time.
Devices that are never online together still converge

There is no server. Each device writes encrypted blocks into storage you own and, next to them, a signed and encrypted ledger of what it did. Another device reads the ledger when it reaches the same storage, verifies the signatures and knows what exists, where it is and which copies were checked by someone else. varsto fsck --verify re-hashes every object and reports claims the storage cannot back. A device restored from an old backup is detected and fenced.
Use case: a laptop that is on the road for a week and a desktop at home. Both write to the same bucket or NAS share whenever they can; they never need to be on at the same time.
Transferrer: a disk that travels between two devices

Mark a USB stick or an external disk as a transferrer. It only receives the encrypted blocks that the other device still lacks, and once both ends hold a block it is removed from the stick. For gigabytes of video between home and office this is faster than any upload, and it works with no internet at all.
Use case: edit footage at the office, carry the stick home, plug it in; the home machine catches up in minutes and the stick empties itself for the next trip.
Untrusted replicas: backup space you do not have to trust

Give a friend, a relative or a rented box a replica token. Their device copies your encrypted objects from a shared location to its own disk, verifies every hash, and reports the copies into your ledger. It never receives a key that could open anything; it learns object names and sizes, exactly what a storage provider learns. Two users can host each other's backups this way.
Use case: you and a friend each keep a copy of the other's vault on a NAS in your homes. Neither can read the other's files; both see in their own app that the copies exist and are verified.
Selective sync with placeholders

Every device can keep a folder in selective mode: the full tree is visible as placeholders, a file is downloaded when you ask for it, and Free up space turns it back into a placeholder once it is safely stored elsewhere. Placeholders are never mistaken for deletions. Right-click Download and Free up space work in Finder, Explorer and the common Linux file managers, and double-clicking a placeholder opens the file; native placeholders (File Provider, Cloud Files) come later. The mechanism is the same as in Resilio Sync's selective sync.
Share a folder with another Varsto user

Sharing is key sharing: the recipient's device prints a request code, the owner seals the folder key to it (hybrid X25519 + ML-KEM-768) and sends the token back over any channel; only the requesting device can open it. The recipient syncs the folder through storage both can reach, and their device writes its own signed ledger under the folder key, so the owner sees their copies too. The token opens that folder and nothing else of the vault. Before sealing, you and the recipient compare six words derived from the request code, over a call or in person, so a code swapped on its way is caught. The Shared page lists who has access, with the words you confirmed; Remove… gives the folder a new key that only you and the members who stay receive, and a token nobody accepted yet can be revoked the same way. QR invitations are the next step.
A real background app on macOS, Windows and Linux

The background service starts at login (a systemd user unit on Linux, a launch agent on macOS, the tray app on Windows) and is set up by the first command once a vault exists. It watches your folders and syncs changes within seconds, with a periodic catch-up for changes made elsewhere; there are no sync, refresh or check buttons to press. The same small binary provides the command line and the local interface, served only to your computer. Updates are looked for automatically and offered only when a newer version exists; installing one checks the release signature and the GitHub checksums, and the macOS app replaces itself from the signed disk image. varsto transfers --watch shows the uploads, downloads and peer traffic running now.
Your own buckets, rclone remotes and cold storage

A storage is a directory, an S3-compatible bucket with your own access keys (AWS, Scaleway, Hetzner, Backblaze B2, Cloudflare R2, MinIO) or any rclone remote, so SFTP, WebDAV, Google Drive and the rest come for free. Secrets stay encrypted on your device; rclone keeps its own. Archive classes such as Deep Archive are written but never read without an explicit confirmation, and the app reports an object that must be restored first instead of retrying. Every storage can carry a price per GB-month, for egress and for restore, set by you or taken from the open price data when the provider, region and class are recognised, so the app shows what each storage and each folder costs a month.
Status: directories, S3 and rclone work; per-storage prices with monthly costs on the Storages page, varsto storage price and varsto storage list. A folder can be written to chosen storages or places only (varsto folder placement), and varsto move (or the "Move to" suggestion) moves its blocks, or those of its idle files, to another storage such as a cold one: copied, checked, recorded, then removed from the old storage, never below the folder's policy and never the last copy, with the change in the monthly bill shown first. Blocks kept only on cold storage are read only after you move them back with a confirmed cold read.
Old disks on a shelf as counted, verified copies

Attach a disk from a USB dock, let the app fill it with the data that has the fewest copies, eject it when told, and store it anywhere. Next time it is attached the app verifies it, repairs what rotted and loads what is new. Disks belong to groups and places, so a policy can require one copy at home and one elsewhere. A folder can be kept only on disks, replicated as many times as you choose, with no cloud copy at all.
Status: the disk pool works: add, fill within a reserve, check (sizes or full re-hash, queued deletions applied), eject, retire; disks are recognised by their marker wherever they appear, and files on a disk that is away say "attach disk data-01 (shelf)". Disk groups keep N copies on disks kept in different places (each disk has a place; disk check fills what a place lacks, policies count each disk copy at its place and report blocks short of the rule), and a folder written only to a pool is a "disks only" folder.
Mobile apps that keep nothing in clear text

Android and iOS run the same encrypted core. Files stay encrypted on the device and are decrypted when you open them; thumbnails are generated once, encrypted and shared with your other devices. The Android alpha is a sideloadable APK with a compact file list (a long press selects files to download or free); the iOS app is built and run in the Simulator on every change and has not run on a real device yet.
Status: in progress. A folder kept encrypted on the phone holds only encrypted blocks there, the same ones your storages hold; selective sync decides which files are kept on the phone, as in any folder, and files added on the phone are encrypted as they arrive. The Android app shows pictures, video (with seeking), audio and text from such folders in its own viewer, decrypted in memory and never written to the phone; PDFs and other files open in another app, which receives a decrypted copy that Varsto removes when it locks or restarts. Camera upload sends new photos and videos to a folder in YYYY/MM subfolders, optionally only on Wi-Fi or while charging. iOS has neither yet.
Post-quantum hybrid cryptography everywhere a public key is used

Signatures are hybrid: every ledger batch carries an Ed25519 signature and an ML-DSA-65 (FIPS 204) signature over the same bytes, and a batch is accepted only if both verify. A key that has a post-quantum part never accepts an Ed25519-only signature, so nobody can strip the stronger half. Key exchange is hybrid too: a share token is sealed to the recipient's X25519 + ML-KEM-768 (FIPS 203) key, so the folder key never travels in clear and the token can be sent over any channel.
Devices created with alpha-0 keep their Ed25519-only keys and stay valid, because every signed object carries an algorithm identifier; nothing stored had to be rewritten. Re-enrol such a device to give it a post-quantum key.
An MCP server: let your assistant read, analyse and tidy, with exactly the access you grant

varsto mcp speaks the Model Context Protocol, so a local model (through Ollama, LM Studio or any MCP client on your own machine), Claude or an IDE assistant can work with your files: read and summarise them, find what belongs together, propose a tidier structure, move and rename files into it, and leave an index or notes, all inside the folders you granted and read-only unless you said otherwise. Strongroom folders are never visible, and everything the assistant writes syncs like any other change. It can never delete or overwrite a file: there is no delete tool, it only creates new files, and moves and renames go only to free names.
Varsto itself keeps the last-used record of every file, merged across your devices so a file counts as idle only if no device used it, and suggests where idle data would be cheapest to keep; the assistant can see that estimate for context, but placement advice is Varsto's own job, not the assistant's.
Durability policies that warn you before they break

Tell a folder what must always be true: "at least two cloud copies and one at home, verified within 30 days". Every folder starts with a default: one copy on any storage, one in external storage, one on your own devices or disks, verified by another device within 30 days. The policy travels with the folder, and every device evaluates it from the signed ledger alone, without asking the others. The app distinguishes ok, at risk (a verification is ageing out, or the only spare copy sits on cold storage or on a disk that is away), violated and unknown, and tells you while there is still time: a notification from the background app, a banner in the interface, and varsto policy check with an exit code for cron or monitoring. On the desktop, a "Where your data is" chart on the Overview draws each folder flowing into the storages and devices that hold it, in proportion to the bytes, with how many copies every block has.
Verification is automatic: the background service on each device re-reads, within a daily budget, blocks that other devices wrote, checks their hash and records it in the ledger, oldest first and long before a window runs out (varsto verify, and on the Policies page). Cold storage is never read for it. fsck --verify and replicas still verify as well. A copy found missing or damaged is repaired automatically from another storage, this device's own files or encrypted blocks, or a peer, and the copies that cannot be repaired raise a notification with the reason (varsto repair; cold storage is read for a repair only when you confirm it). Storage places are labels you give when adding a storage.
Devices that send each other the blocks, torrent-style

Peer-to-peer is on by default on every device (port 17893; varsto p2p disable turns it off). A new file is announced before its upload, so your devices on the same network fetch it directly while the copy to the storages is still on its way. Every device that has a file can serve its encrypted blocks, byte for byte the same objects the storages hold. A device that needs a block asks its peers first and the cloud second, checks every block against its content hash, and spreads the work over the peers that answer. On the LAN devices find each other by themselves; across the internet they learn their public address from STUN, punch through NAT over QUIC with a certificate pinned per device, and when punching fails they go through one of your own reachable devices (a home server, a forwarded port, a VPS), which sees only ciphertext. Only a holder of the vault key can fetch anything, and what travels is ciphertext. A live traffic view on the Peers page (and varsto p2p traffic --watch) shows which device is sending to which, over which path and how fast, including what a device relays for two others. Measured across three countries: Benchmarks.
Blocks are compressed before encryption (zstd), so every transfer and every copy is small, on the LAN as on the internet. NAT traversal is tested on localhost and on the maintainer's own networks only; a vault with every device behind NAT has no path across the internet yet.
Strongroom: folders that open only with your security key

A Strongroom folder's key is never stored anywhere. It is wrapped under a secret that only your FIDO2 security key can produce (the hmac-secret extension), so a touch of the same key opens the folder on every device of the vault, and nothing else does: not your passphrase, not the vault key, not a stolen laptop. Enforcement is cryptographic, not a dialog. Unlock for a window, work, lock; while locked the folder is skipped by sync, cannot be shared, and is invisible to assistants.
Enrol a backup key, say a second YubiKey kept in a safe: each key wraps the same folder key, and either one opens it. An existing folder can become a Strongroom: it gets a new key, everything is re-encrypted and uploaded again, the old copies are deleted from your storages once the new ones are in place, and your other devices swap their plain copies for placeholders on their next sync.
Needs the libfido2 tools (fido2-cred, fido2-assert); a software key exists for trying the flow. Touching the key happens on the command line (varsto strongroom convert, add-key, rekey); the interface shows the command and lists the enrolled keys. A device that already had the old key could have kept it; removing a key does not re-key the folder, varsto strongroom rekey does.
A recovery kit for paper or metal
There is no account and no escrow: the vault key is yours alone, so the app helps you keep it. varsto recovery kit prints the key as 24 words with a checksum, laid out for paper or metal, and optionally three shares of which any two rebuild the key and one alone reveals nothing, so no single place has to hold everything. A new device joins straight from the words. Test it once a year.
Remove a lost or stolen device, and wipe it remotely

From any other device, Remove device signs a revocation into your storage. Every device then ignores the removed one's ledger entries after the cut-off and refuses its peer connections, and the vault moves to a new key that is sealed (X25519 + ML-KEM-768) to each remaining device only: ledger, records, manifests and new files of every folder use keys the removed device never sees. With a wipe order, the device deletes its keys, sync state and folder contents the next time it reaches a storage; the order is signed by one of your devices, so a storage or someone with an old vault key cannot trigger it.
What the removed device could read before stays readable to it; folders shared with other people and Strongroom folders keep their keys; storage credentials are not rotated for you. Print a new recovery kit afterwards.
Organizations: administrators, approvals and a signed log, for business use
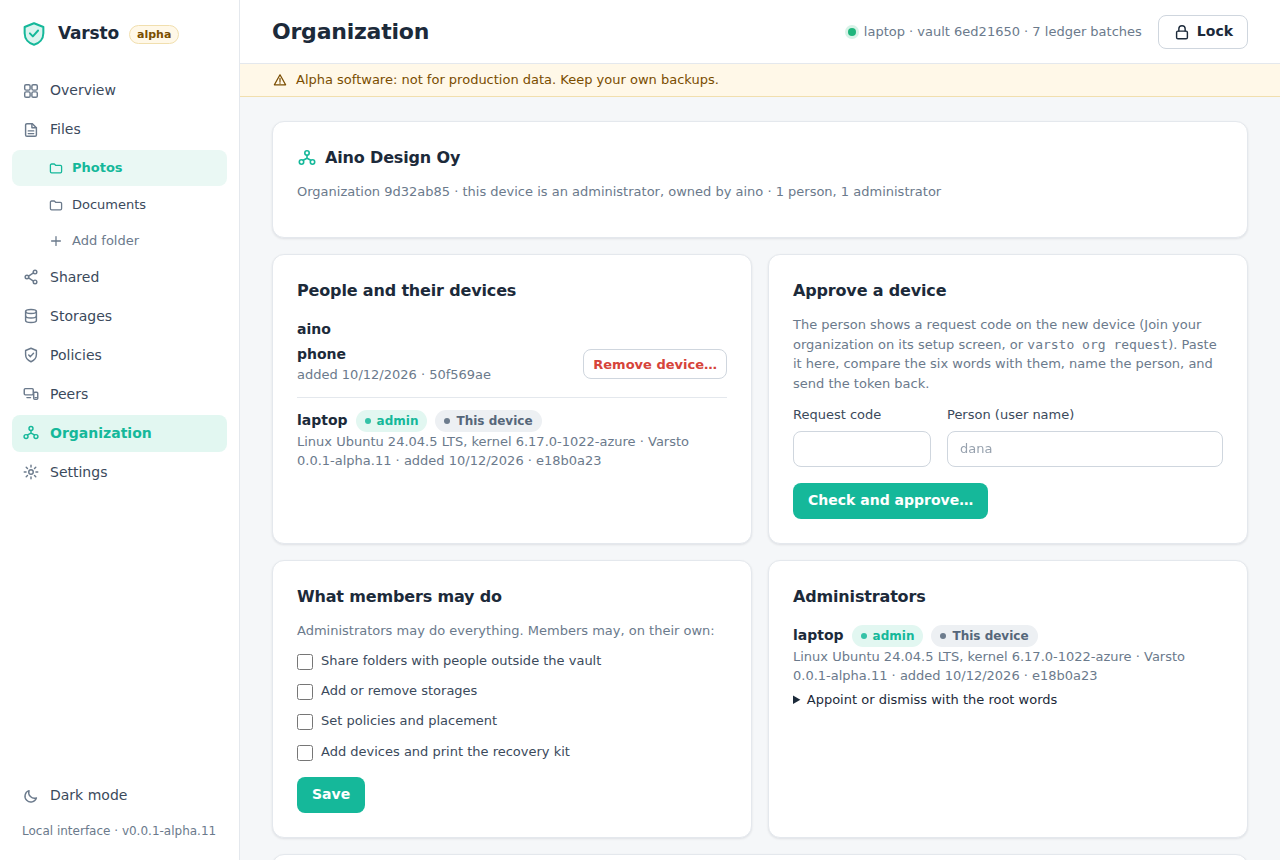
Use case. A small firm keeps its project folders in its own bucket. The office manager is the administrator: a new employee installs Varsto, sends a request code, and the manager compares six words with them on the phone and approves the laptop. When someone leaves, one action removes them and every device of theirs, and the remaining devices get new keys.
A vault has devices, not people, and every full device is equal. An organization adds the layer a company needs: administrators who approve devices for named people, remove a person with every device of theirs in one step (the vault gets new keys that only the remaining devices receive; with a wipe order the removed devices delete their keys and folder contents), set what members may do on their own (share outside the vault, add storages, set policies, add devices), and keep a log of it that is signed by their devices and chained, so nobody can change it afterwards unnoticed. A device joins with a request code and a six-word fingerprint the administrator compares with the person; the approval token, sealed to that device's key, carries the vault key and the storage settings. A device that joined with the vault key alone is ignored by the others until an administrator adds it. The root key that appoints administrators is 24 words on paper, never on a device.
Getting started. Use with a team under Settings, or varsto org create --name … --user …, turns a vault into an organization; the devices it already has become the founder's devices, and the device that creates it is the first administrator. The Organization page lists people and their devices, approves new ones, sets what members may do, appoints or dismisses administrators with the 24 root words, and shows the signed log (exportable as JSON); members see the page without the administrator actions. Only administrators can remove devices, and peers refuse devices that are not in the roster.
A vault without an organization is unchanged: no new objects, no new checks, nothing in the interface beyond the Use with a team card in Settings. Storage credentials are still shared and not rotated, existing data is not re-encrypted after a removal, and there is no second factor on administrator actions yet.
Also in the design
- QR invitations for sharing.
- Per-device storage credentials, rotated at the provider when a device is removed.
- Re-encrypting existing data after a device is removed.
- Packs for small files.
- Incremental manifests.
- DHT peer discovery.
- Proof-of-storage challenges.
- Erasure coding across storages.
- Encrypted, redacted logs.
- A File Provider / Cloud Files integration for placeholders.
- iOS camera upload and viewer.
- A second factor for device enrolment.
Every design document on the Docs page says which parts exist. Nothing has been audited yet.